All docs pages (49)
Explain Access
Trace a user's object and field access back to the profile, permission set, group or muting set behind it, see who can read a field, and compare two users.
Updated 2026-06-08
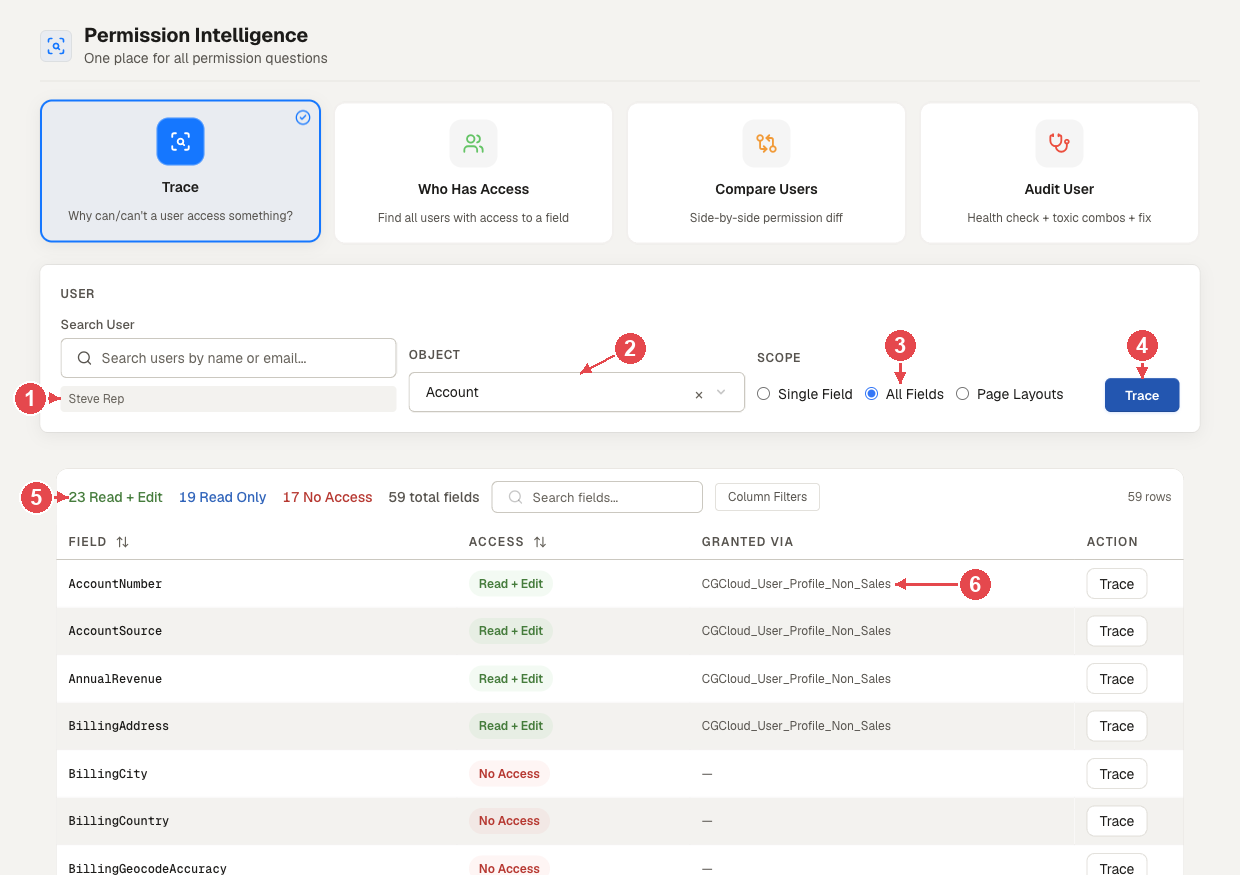
Find it in the sidebar as Explain Access. Up to version 1.1.13 it was called Permission Intelligence (and before that, Permission Chain); only the name changed, so old links and bookmarks still open it. It answers the question every admin dreads: "why does this user have this access?" It traces a user's access to an object or field back through each layer and shows the grant responsible, so you can fix the source instead of guessing.
It has three modes: Trace, Who Has Access and Compare Users. Version 1.1.13 also has Audit User; in the release after 1.1.13 that check moved to Security Insights → Users → Check. It only reads; it never changes permissions.
Top screenshot: 1 The user you picked. 2 Object. 3 Scope, here All Fields. 4 Trace. 5 Count of fields by access. 6 The profile or permission set that grants the access.
The layers it walks
Effective permissions in Salesforce are the sum of several layers. Explain Access walks each of them and records where every grant comes from:
- the user's Profile
- each assigned Permission Set
- each Permission Set Group the user belongs to
- any Muting Permission Set that removes permissions inside a group
Trace covers object access and field-level security. Pick a user and an object, then trace one field, every field on the object, or the object's page layouts. You see not just whether the user has the access, but which assignment grants it. "Granted via the Sales Ops permission set" is an answer you can act on; "they have it somehow" is not.
In the release after 1.1.13, Trace has a fourth scope, Object Permissions: each of the seven object permissions (Create, Read, Edit, Delete, View All, Modify All, View All Fields) for the user on the object, granted or not, with every profile, permission set or group that grants it, including View All Data and Modify All Data.
User and system permissions (for example API Enabled) are not traced here.
Muting permission sets are detected by key prefix (
0QM), not by relationship name, so muted permissions are attributed correctly even where the standard relationship returns null.
Who Has Access
Run the question in reverse. Start with an object and a field, and ask which users can read or edit it. You get the list of users, with the grant path for each. It fits "who can see Social Security Number?" style audits.
In the release after 1.1.13 it also answers for an object permission (for example, who can delete Accounts) and a system permission (for example, who has Modify All Data), with where each user gets it.
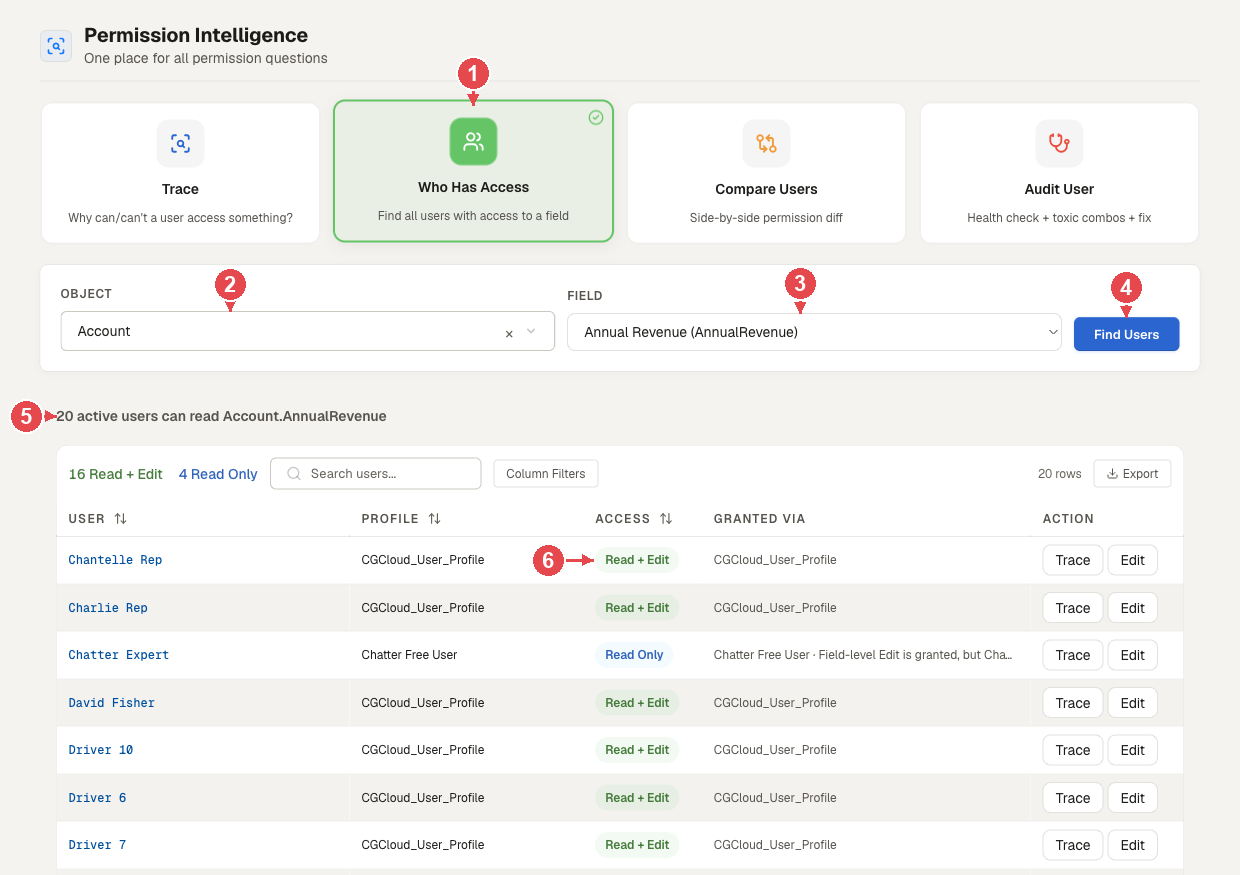
1 The Who Has Access mode. 2 Object. 3 Field. 4 Find Users. 5 The answer in one line. 6 Each user's access.
Compare Users
Put two users side by side and see where their access differs, object by object and permission by permission. Use it to answer "what does this new hire lack compared with that rep?", or to explain why two people on the same team see different things.
Comparisons download as CSV or JSON, or copy to the clipboard as CSV or TSV, so a permission difference becomes evidence you can attach to a ticket.
In the release after 1.1.13 the same comparison is also the Users tab of Compare.
Audit User (version 1.1.13)
Pick one user for a health check: risky permission combinations they hold and suggested fixes. In the release after 1.1.13 this is the Check button on a user in Security Insights → Users, with the same checks; a fix still asks before it changes anything.
When to reach for it
- A user can see something they should not: find the grant and remove it.
- A user cannot do something they should: find the missing grant and add it.
- Onboarding: compare a new hire with an existing user to see what is missing.
- Audit: show who can reach sensitive fields, and why.
Related reading
- Why can this user see this record?
- Persona Simulator: combine a profile and permission sets and see the access, page layouts and app access they give.
- Security Insights: org-wide view of risky permissions.