All docs pages (49)
Security Insights
Your org's security posture in one place: a score across six dimensions, risky permission combinations, per-user blast radius, connected apps and field checks.
Updated 2026-06-08
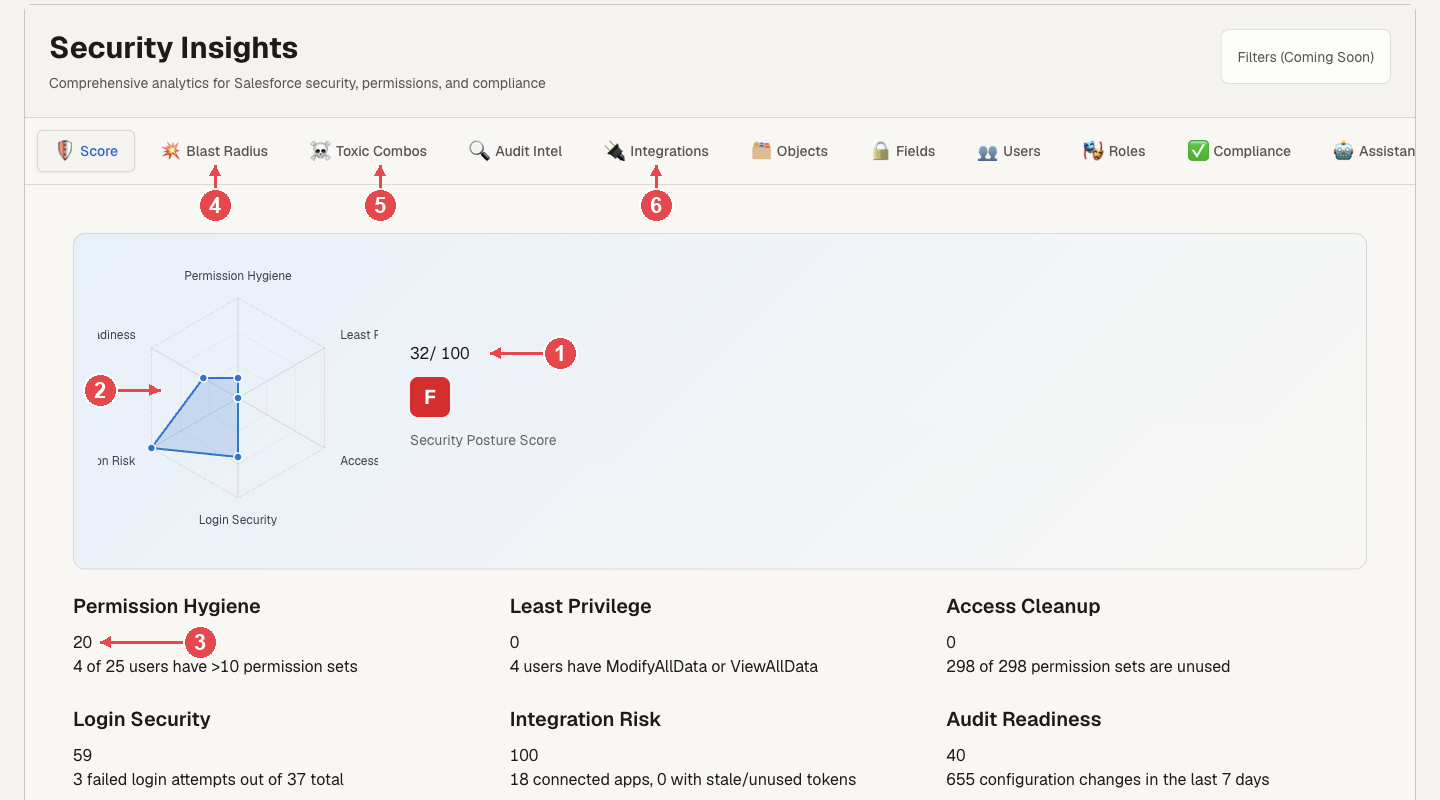
Security Insights turns the question "is our org secure?" into a dashboard you can read. It reads the permission sets, permission set groups and profiles assigned to active users, and shows the accounts and combinations that put the org at risk, with the user and their permission sets attached so you can act.
It reads at most 2,000 permission set assignments of active users. In a larger org, assignments past that limit are not read, so some users may be missed, and the page does not warn you.
Top screenshot: 1 The posture score. 2 The six-dimension chart. 3 One dimension's score and reason. 4 Blast Radius tab. 5 Toxic Combos tab. 6 Integrations tab (connected apps).
Posture score
The Score tab shows one posture score from 0 to 100 with an A to F grade. It is a weighted average of six dimensions:
- Permission Hygiene: how many active users hold more than 10 permission sets.
- Least Privilege: how many active users have Modify All Data or View All Data.
- Access Cleanup: how many permission sets are assigned to no active user.
- Login Security: the share of failed logins in the last 30 days.
- Integration Risk: stale or unused OAuth tokens compared with your connected apps.
- Audit Readiness: how many setup changes were made in the last 7 days.
If a dimension cannot be read (for example, your user cannot query login history), it scores 50 and says it could not be assessed. Use the score to find the findings below, not as an audit result on its own.
God mode
Security Insights flags a user as God Mode when they hold Modify All Data, View All Data and Manage Users together. Permissions are combined across the profile and every assigned permission set, so a user who gets each one from a different place is still flagged.
The Least Privilege dimension separately counts users with Modify All Data or View All Data.
For background on why this matters, see How to find every god-mode user in your org.
Toxic combinations
Some permissions are dangerous only together. The Toxic Combos tab checks these:
- God Mode (critical): Modify All Data + View All Data + Manage Users.
- Admin Takeover (critical): Manage Users + Author Apex. Create admin users and deploy code.
- Data Exfiltration Risk (high): View All Data + Run Reports. See everything, then export it in reports.
- Modify + Customize (high): Modify All Data + Customize Application. Change both data and configuration.
- Password Bypass (high): Password Never Expires + Modify All Data. Skipped if the org does not expose that permission.
- Inactive God (medium): no login in the last 90 days (or never), but still holds Modify All Data or View All Data.
- Permission Stacking (medium): more than 10 permission sets.
- External Overprivilege (medium): an external or community user with Modify All Data, View All Data or Manage Users.
Each finding lists the affected users, their permission sets and suggested fixes.
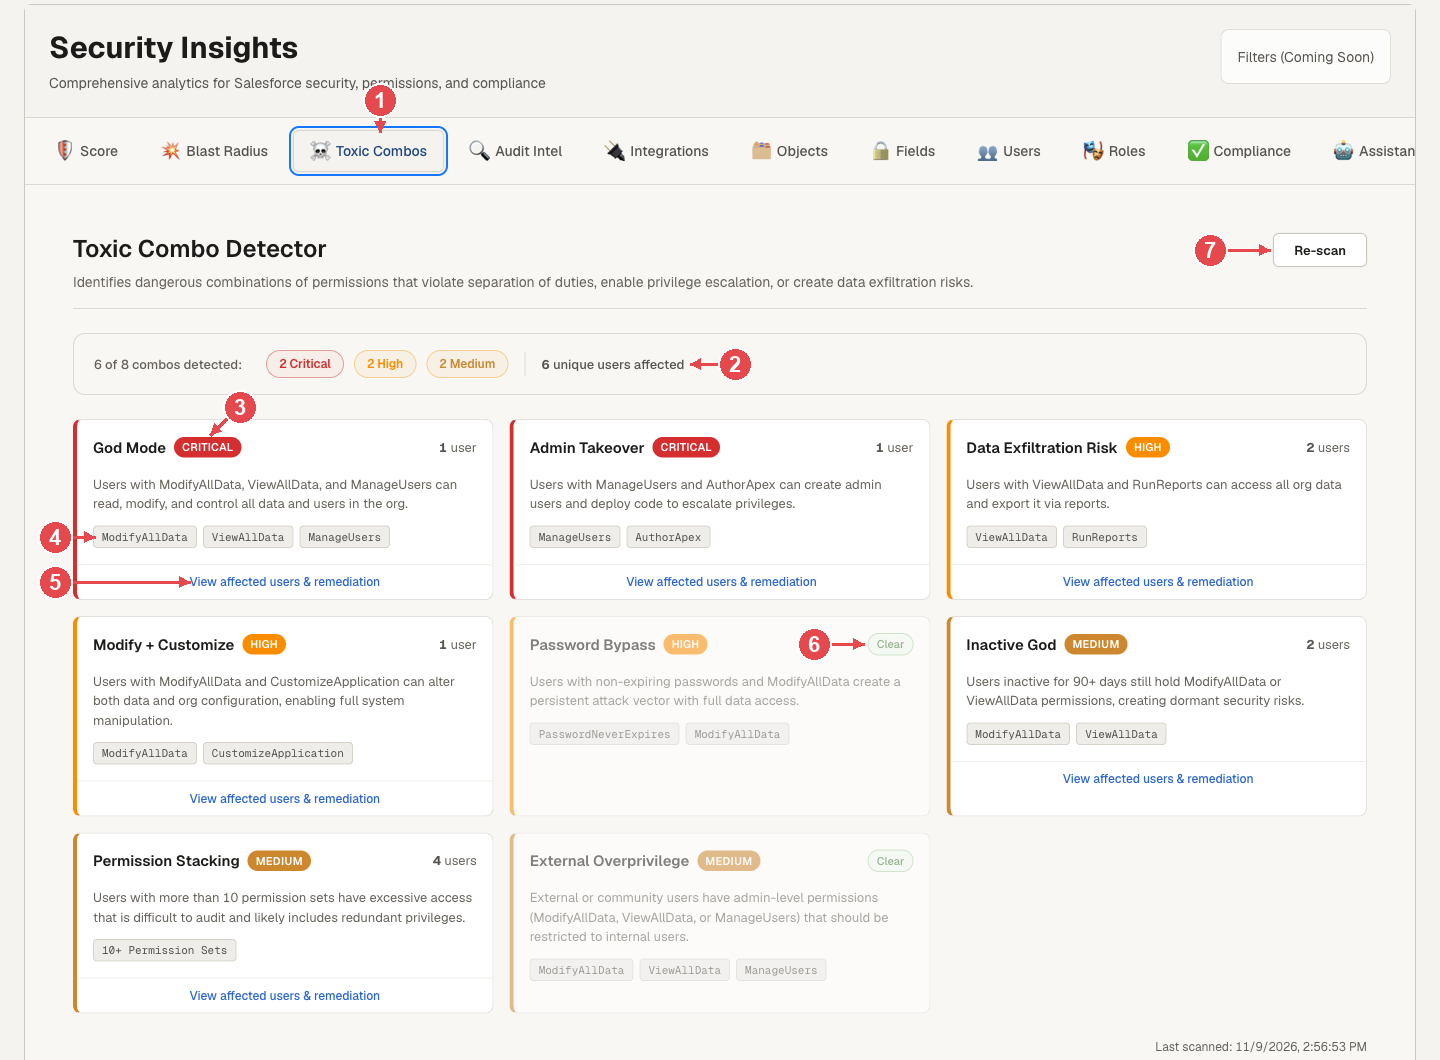
1 Toxic Combos tab. 2 Summary of combinations detected and users affected. 3 Severity of a combination. 4 The permissions that make it toxic. 5 Link to the affected users and remediation. 6 A combination with no users shows Clear. 7 Re-scan.
Blast radius
Search for one user to see their blast radius: every object they can reach, with create, read, edit, delete, View All and Modify All, and the permission set that grants each one. It counts objects, not records. Here a user is marked God Mode if any of their permission sets or their profile has Modify All Data, a looser rule than the Toxic Combos check above.
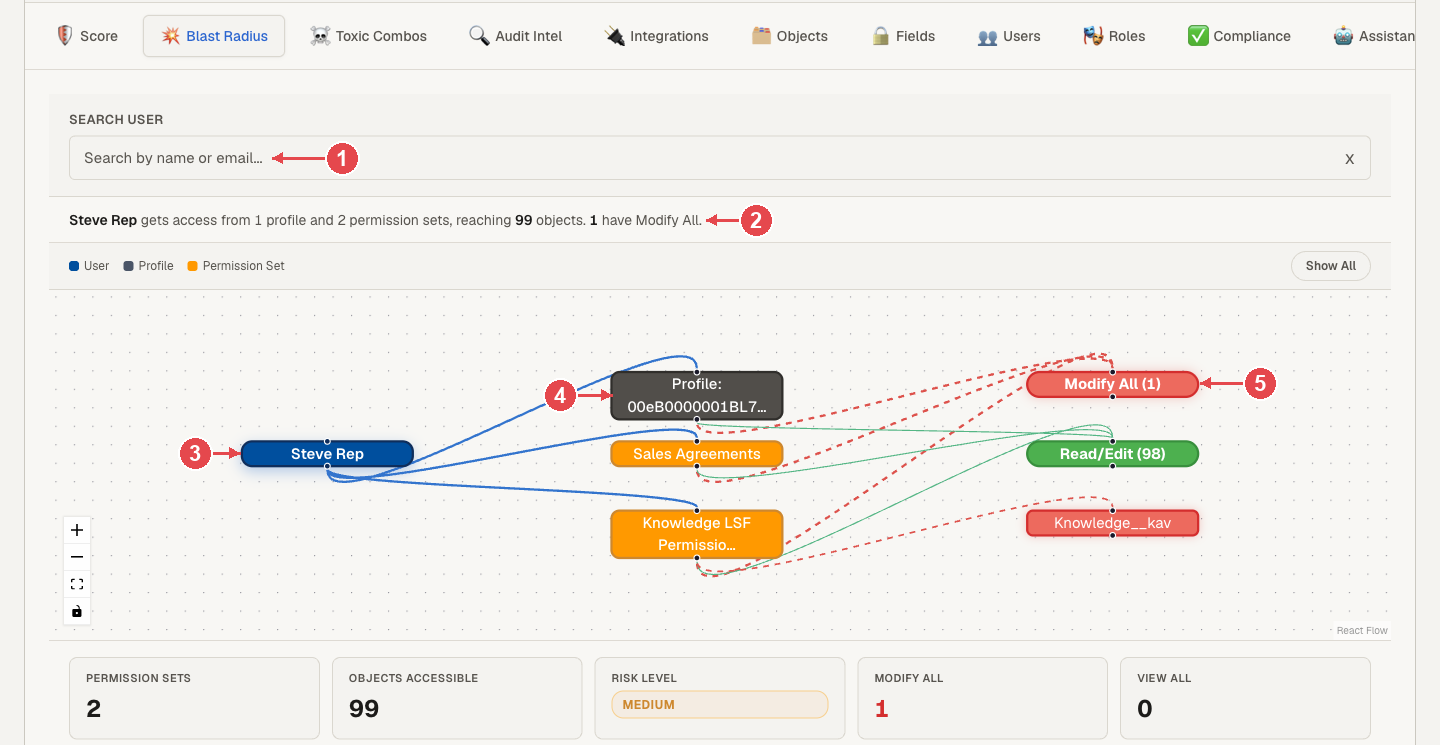
1 User search. 2 One-line summary of what the user reaches. 3 The user. 4 The profile and permission sets that give access. 5 The objects reached, here with Modify All.
Check one user
In the release after 1.1.13, each row of the Users tab has a Check button (and Check a user finds anyone else). It opens a panel with that user's health check, risky permission combinations and suggested fixes, plus a link to their Blast Radius. A fix asks you to confirm first and is never applied on its own. It replaces the Assistant tab of version 1.1.13 and the Audit User mode of Explain Access.
Where findings come from
The blast radius names the permission set or profile that grants each object. Toxic combination findings list all of a user's permission sets; they do not say which one grants the risky permission, so check those permission sets to find it.
Beyond permissions
Security Insights also reviews connected apps (OAuth tokens and third-party access into the org) and has field-level analytics: field-level security coverage per object, and editable fields that no permission set or profile has field-level security for.
Related reading
- Explain Access: trace a user's object or field access to its source.
- Persona Simulator: preview the access a profile and permission sets give, before and after a change.
- Org Health: broader org checkups, including permission debt.